AI is already in your business.We don’t sell AI tools, and we don’t argue against AI. We govern its use.
Staff use AI tools, more each year, often with no written rules. That leaves each person to decide what data goes into which tool. So we start with what is happening now: which tools are in use, by whom, and with what data. Then we write the rules for it with the owner.
Code alone misses the cases no one wrote a rule for, and AI alone can be confidently wrong. So each workflow is a series of steps. Code does what rules can do. Where the work needs judgment, AI gets one narrow job and answers in a set format, citing its source, so code or the person who knows the job can check it before the next step uses it. The goal is AI work that is visible, reliable and accountable. Done responsibly, it supports the staff who already do the work.
We serve as the vCISO (an outside security officer) for small businesses that hold sensitive client information in confidence, and bring secure, governed AI into their work along the way. Accounting offices, law offices, medical practices and insurance agencies across the Stateline area, in Illinois and Wisconsin.
A few of the things a vCISO does for the office:
- Serves as the named security lead a rule calls for: the Safeguards Rule’s Qualified Individual, or HIPAA’s security official
- Writes the AI acceptable use policy, device use policy and code of conduct with the owner, and keeps them current
- Maintains the WISP and the risk assessment behind it
- Helps answer cyber-insurance applications, security questionnaires and client due-diligence requests
- Reviews security and data terms with counsel: DPAs, BAAs, vendor agreements and AI terms of service
- Runs third-party risk reviews on vendors and AI tools, shadow AI included
- Builds the incident response plan, runs the annual tabletop exercise and responds the same day
- Governs AI workflows: human in the loop, every answer cited to its source
The rest depends on the office. The Audit maps it.
Local, on site and in person.
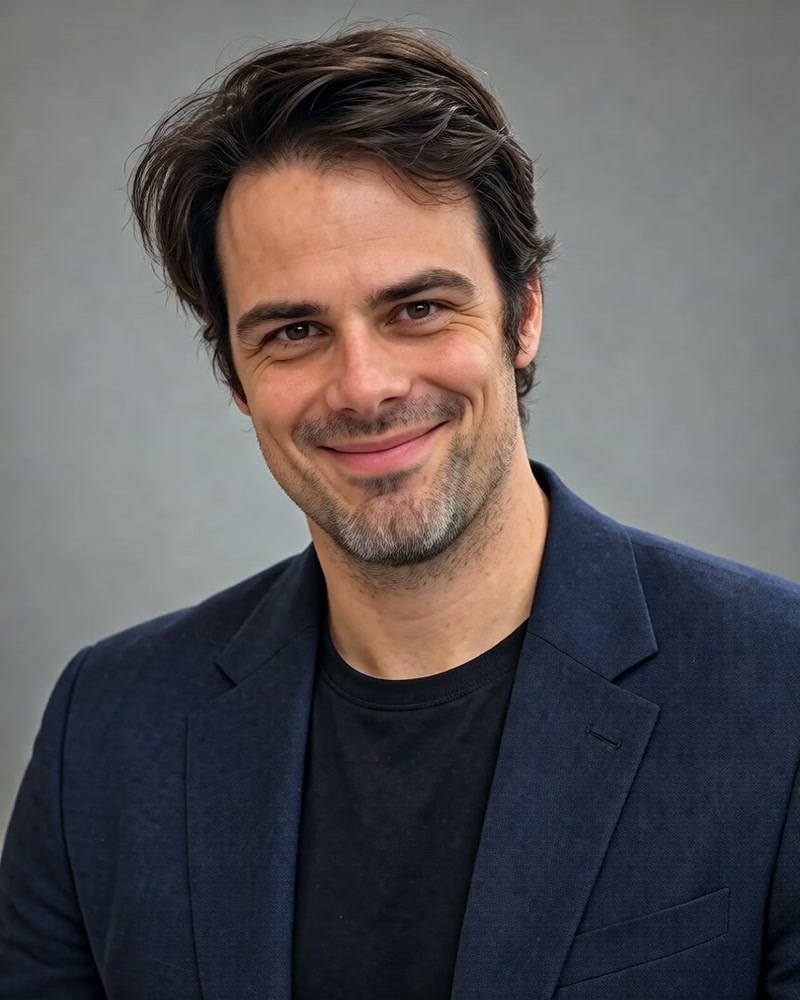
Pete Saar has fifteen years in cyber security. He holds the CISSP, with GIAC certifications in incident handling and forensics. He was formerly TS/SCI-cleared, and he is a Coast Guard veteran. He has engineered and governed agentic AI at enterprise scale. Now he brings that experience to local businesses in the Stateline area.
He was born and raised in Northern Illinois, where he lives with his wife and son. He spends his free time hiking, canoeing and enjoying the outdoors. Working close to home means meeting in person, which he prefers.
Map it. Build it. Run it.
Each step stands on its own. If the office stops after any one, it keeps what it paid for.
- The Audit
Map it
The Audit looks at what is in use, what is exposed, and where AI can take on real work first. It starts with a meeting, at no charge. An engagement letter follows, with the scope and a fixed fee. The work then takes two to three weeks, and little of it is the office’s time. The owner then knows where the business stands.
The business keeps a written report of findings. It is an outside assessment to show a vendor, a partner, an insurer or an attorney, and the record to point to when the cyber-insurance renewal asks about AI and data handling. The Audit fee is credited toward the Sprint if the Sprint is signed within 60 days of the Audit report.
- The Sprint
Build it
We close the gaps alongside the IT provider already in place. The rules for AI become the business’s AI use policy. Then the first AI workflow goes to work on a real job, with its answers checked against their sources.
The business keeps a clean baseline and an attestation of remediation, finding by finding. The first improvement is built onto the clean record.
- The Retainer
Run it
Each month we work inside the business as its vCISO. The next improvement gets built when the business is ready, sized to fit, and the time each one saves is measured. The written information security program (the WISP), vendor risk and vendor contracts are kept current. New vendor and partner negotiations are checked for security and data terms. The fee is flat and monthly, set by the size of the business.
The business keeps a current record and the numbers on every improvement. It also keeps a named security lead, a plan for the day something goes wrong, and a current attestation whenever it asks for one. Each month has at least one visit in person and one check-in.
A report anyone can check.
Every report is registered the day it is issued. The business may share it with its lawyer, its insurer or its board. Any of them can confirm on the Verify page that the copy in hand is the one we issued, unchanged.
- What comes backwhere things stand, and what to improve first
- Every findingtied to the rule it comes from
- Never a finding fromwhat the business told us alone
- Scopewhat we looked at, and what we didn’t
Sample documents.
These are sample documents for a fictional business, Riverbend Tax & Books. They use the same format a real engagement produces. They run from the first findings to the attestation of remediation, then one period of the Retainer after it. Nothing in them is about a real business.
- The AI & Security Auditfindings report · 25 pages · PDF
- The AI & Security Sprintthe record of what was fixed · 12 pages · PDF
- Attestation of remediationthe follow-up review, finding by finding · 2 pages · PDF
- The AI & Security Retainerthe record of one Retainer period · 16 pages · PDF
Start with a meeting.
The first meeting runs fifteen to thirty minutes. We listen to what the business needs, what’s getting in the way and what it’s working toward, then talk through what the work would involve and whether it’s a fit for both sides.
Request a consultation